

ISO 42001 Certification Body
The Definitive Guide to ISO 42001 : 2023 by IFGICT
Artificial intelligence has officially transitioned from experimental laboratories into the core engine of global commerce, infrastructure, and public administration. Yet, with immense power comes unprecedented complexity. Organizations everywhere are racing to deploy machine learning models, generative tools, and automated decision-making architectures. However, they face a critical bottleneck: how to prove that their AI systems are ethical, transparent, secure, and compliant.
Enter the benchmark standard for artificial intelligence management: ISO 42001 : 2023.
As a premier global authority, the International Federation of Global & Green ICT (IFGICT)—an independent organization recognized and listed by the United Nations (UN), alongside being an active partner to the International Telecommunication Union (ITU) and the Institute of Electrical and Electronics Engineers (IEEE)—serves as a leading certification body. IFGICT is defining ISO 42001 : 2023 compliance for enterprises worldwide, establishing trusted pathways for secure, sustainable digital transformation.
Understanding the Foundation: What Is ISO 42001 : 2023?
The rapid acceleration of generative AI and automated systems caught many regulatory frameworks off guard. To bridge this gap, international standards organizations introduced ISO 42001 : 2023 as the world’s first artificial intelligence management system (AIMS) standard.
Unlike traditional software guidelines, ISO 42001 provides a comprehensive framework for organizations to responsibly develop, provide, or utilize AI systems. It covers the entire lifecycle of artificial intelligence—from initial data collection and algorithm design to deployment, risk assessment, and continuous monitoring.
Why Traditional IT Frameworks Fall Short
For decades, standard information security protocols (such as ISO 27001) managed data integrity and confidentiality. However, artificial intelligence introduces unique variables that traditional IT governance cannot solve alone:
Algorithmic Bias: Machine learning models can inherit, amplify, or create biases based on flawed training inputs.
Opacity and “Black Box” Dynamics: Many advanced neural networks make decisions that are difficult for human operators to trace or explain.
Dynamic Learning: Unlike static software code, machine learning models can evolve over time based on new data inputs, requiring ongoing oversight.
By implementing ISO 42001 : 2023 through a trusted certification body like IFGICT, organizations establish a formalized system to manage these unique operational risks.
The Role of IFGICT as a Global Certification Body for ISO 42001 : 2023
Achieving compliance requires more than downloading a checklist; it demands rigorous validation by an accredited authority. As an independent organization listed by the United Nations as a certified service provider, and working closely alongside the ITU and IEEE, IFGICT provides elite-tier evaluations.
The IFGICT Advantage in AI Governance
When organizations pursue ISO Ai certification through IFGICT, they unlock distinct strategic advantages:
UN-Aligned Credibility: Because IFGICT is trusted by international bodies like the UN, achieving an ISO Ai credential signals to global stakeholders that your organization adheres to the highest standards of transparency and corporate responsibility.
Rigorous Auditing Protocols: An official ISO Ai audit conducted by IFGICT-certified professionals evaluates not just the technology, but the organizational culture, accountability lines, and risk management structures surrounding the AI deployment.
Integration with Green ICT: True digital transformation must be sustainable. IFGICT uniquely bridges artificial intelligence governance with green energy metrics, ensuring that power-heavy data centers and AI training models align with global ecological targets.
Core Pillars of an ISO 42001 Ai Management System
To successfully pass an ISO Ai audit, enterprises must embed specific operational pillars into their corporate DNA. Let us examine the structural requirements mandated by ISO 42001 : 2023.
1. Context of the Organization and Stakeholder Analysis
An effective AI management system begins with mapping out who is affected by your algorithms. Organizations must identify internal and external stakeholders—including customers, employees, regulators, and vulnerable communities—and document how the AI system impacts them.
2. Leadership and Commitment
Governance starts at the top. ISO 42001 : 2023 requires executive leadership to actively champion ethical AI policies. CEOs and board members must allocate adequate resources for bias testing, data curation, and continuous model monitoring.
3. AI Risk Assessment and Treatment
You cannot eliminate risk entirely, but you can systematically manage it. Organizations must perform deep-dive risk assessments focusing on:
Data poisoning and cyber vulnerabilities.
Unintended discrimination or disparate impact on protected groups.
Intellectual property and copyright infringement in training datasets.
4. Data Quality and Provenance
Garbage in means garbage out. Under ISO 42001 : 2023, managing the provenance, legality, clean extraction, and continuous cleansing of training data is mandatory. This protects companies from costly legal liabilities and reputational damage.
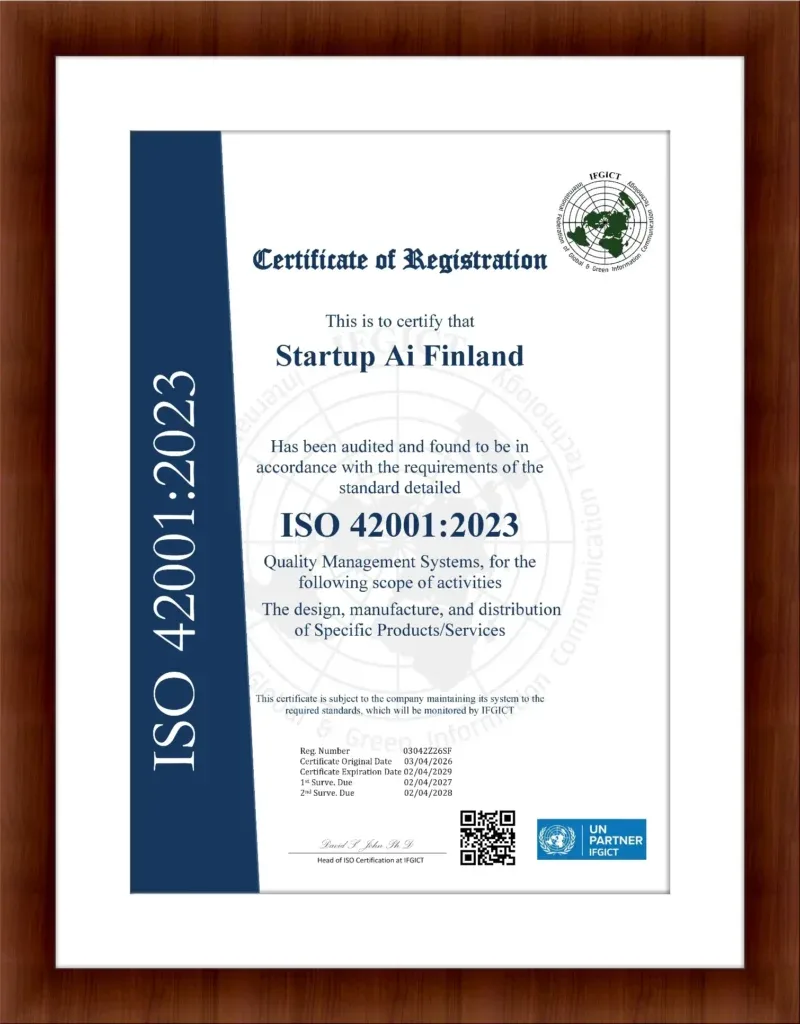
Deep Dive Into the ISO 42001 : 2023 Certification Processes with IFGICT
Securing formal validation for your artificial intelligence management system is a rigorous, highly disciplined journey. As a leading international certification body recognized and listed by the United Nations (UN), and an active partner to the International Telecommunication Union (ITU) and the IEEE, the International Federation of Global & Green ICT (IFGICT) administers a standardized, transparent multi-stage evaluation lifecycle.
This section breaks down the end-to-end operational phases required to successfully navigate an ISO Ai audit and attain full ISO Ai certification under the authority of IFGICT.
Phase 1: Strategic Scoping and Readiness Assessment
Before formal auditing can begin, an organization must define the exact boundary of its artificial intelligence systems.
Defining the Scope: Not every company needs to certify every line of code simultaneously. Organizations can scope their ISO 42001 : 2023 management system to specific business units, generative AI tools, predictive analytics suites, or automated customer service pipelines.
Pre-Assessment Gap Analysis: Conducted either internally or via preliminary consultancy, this step evaluates existing data governance policies, model training records, and human oversight mechanisms against ISO 42001 requirements to surface vulnerabilities early.
Phase 2: Documentation and Control Implementation
An effective ISO Ai framework relies heavily on documented evidence rather than verbal assurances. During this implementation window, enterprises must produce and operationalize core governance documents:
AI Ethics and Policy Statements: Clear declarations approved by executive leadership outlining the organization’s commitment to fairness, non-discrimination, transparency, and data privacy.
Risk Treatment Plans: Comprehensive matrices detailing how the company identifies, mitigates, and monitors potential model failures, security breaches, and unintended societal biases.
Lifecycle Traceability Logs: Rigorous logs capturing dataset sources, version control, hyperparameter modifications, and validation testing results throughout the machine learning development lifecycle.
Phase 3: Stage 1 Audit (Document Review and Readiness Verification)
Once the internal management system is fully deployed and active (typically requiring at least a few months of operational data), the official IFGICT evaluation process commences with the Stage 1 Audit:
The Review: Independent, accredited auditors from IFGICT examine your structural documentation, policies, risk assessments, and resource allocations.
The Objective: To verify that the design of the ISO 42001 : 2023 management system complies fully with international standards and is ready for operational inspection.
Outcome: The auditors provide a formal readiness report. If documentation gaps or policy omissions are identified, the organization is given a defined window to remediate them before advancing.
Phase 4: Stage 2 Audit (On-Site and Deep Operational Inspection)
The Stage 2 Audit represents the core verification phase of the ISO Ai audit journey:
System Testing: IFGICT auditors conduct interviews with executive leaders, data scientists, legal advisors, and IT administrators to ensure the written policies are actively practiced on the ground.
Evidence Inspection: Auditors review real-world AI deployment cases, assessing how risk treatments were executed during live model training, testing, and monitoring phases.
Validating Accountability: Auditors check whether human-in-the-loop overrides function properly and whether incident response protocols are triggered correctly when an AI model exhibits erratic or biased behavior.
Phase 5: Certification Decision and Issuance
Upon successful completion of the Stage 2 evaluation, the audit findings undergo independent technical review by the senior committee at IFGICT.
Awarding the Credential: Upon final approval, the organization is officially granted the ISO Ai certification, validating that its artificial intelligence practices meet globally benchmarked standards.
Global Recognition: Because the credential is backed by a UN-listed body and aligned with IEEE and ITU partnership standards, it carries immense weight in international trade, vendor procurement, and regulatory compliance.
Phase 6: Surveillance Audits and Continual Improvement
Achieving ISO 42001 : 2023 is not a static finish line; it is an ongoing commitment to excellence.
Annual Surveillance Reviews: To maintain active certification, IFGICT conducts periodic surveillance audits (typically annually) to verify that the AI management system is continuously updated and adapting to new algorithmic trends.
Recertification: Every three years, a comprehensive recertification audit is performed to ensure the organization’s governance framework scales effectively alongside rapid advancements in artificial intelligence technology.
Frequently Asked Questions (FAQ)
What is the primary purpose of ISO 42001 : 2023?
The primary purpose is to provide a unified, internationally recognized framework for managing artificial intelligence systems responsibly. It helps organizations balance innovation with ethical guardrails, risk management, and regulatory compliance.
Why choose IFGICT for an ISO Ai audit?
IFGICT is an independent global federation listed as a certified service provider by the United Nations, alongside maintaining strategic partnerships with major international entities like the ITU and IEEE. Their specialized expertise ensures that your ISO 42001 : 2023 credential carries global weight and credibility.
How long does it take to secure ISO Ai certification?
The timeline varies depending on the organization’s current maturity level, size, and complexity of AI deployments. Typically, the process ranges from 3 to 9 months, encompassing gap analysis, policy deployment, internal testing, and the final IFGICT evaluation.
Is ISO 42001 mandatory for all businesses?
While adoption is voluntary for many commercial sectors, an increasing number of government contracts, public tenders, and institutional partnerships now require verified ISO Ai compliance to mitigate systemic liability.
Checkout ISO Certification Body